DON’T MISS DFIR EVIDENCE
Automated Ingest pulls in every source of investigation data.
Your DFIR evidence engine.
Automated Ingest imports data from any relevant source and launches its own DFIR collections with one click.
Start every investigation with every lead.
ACCESS ALL YOUR DATA
Cyber Triage connects to your tech stack and pulls in all relevant data for analysis. This includes other collectors like KAPE, EDRs like Defender, and disk imagers like FTK.
The result: Your conclusions are based on all the evidence.

EASILY COLLECT DFIR ARTIFACTS
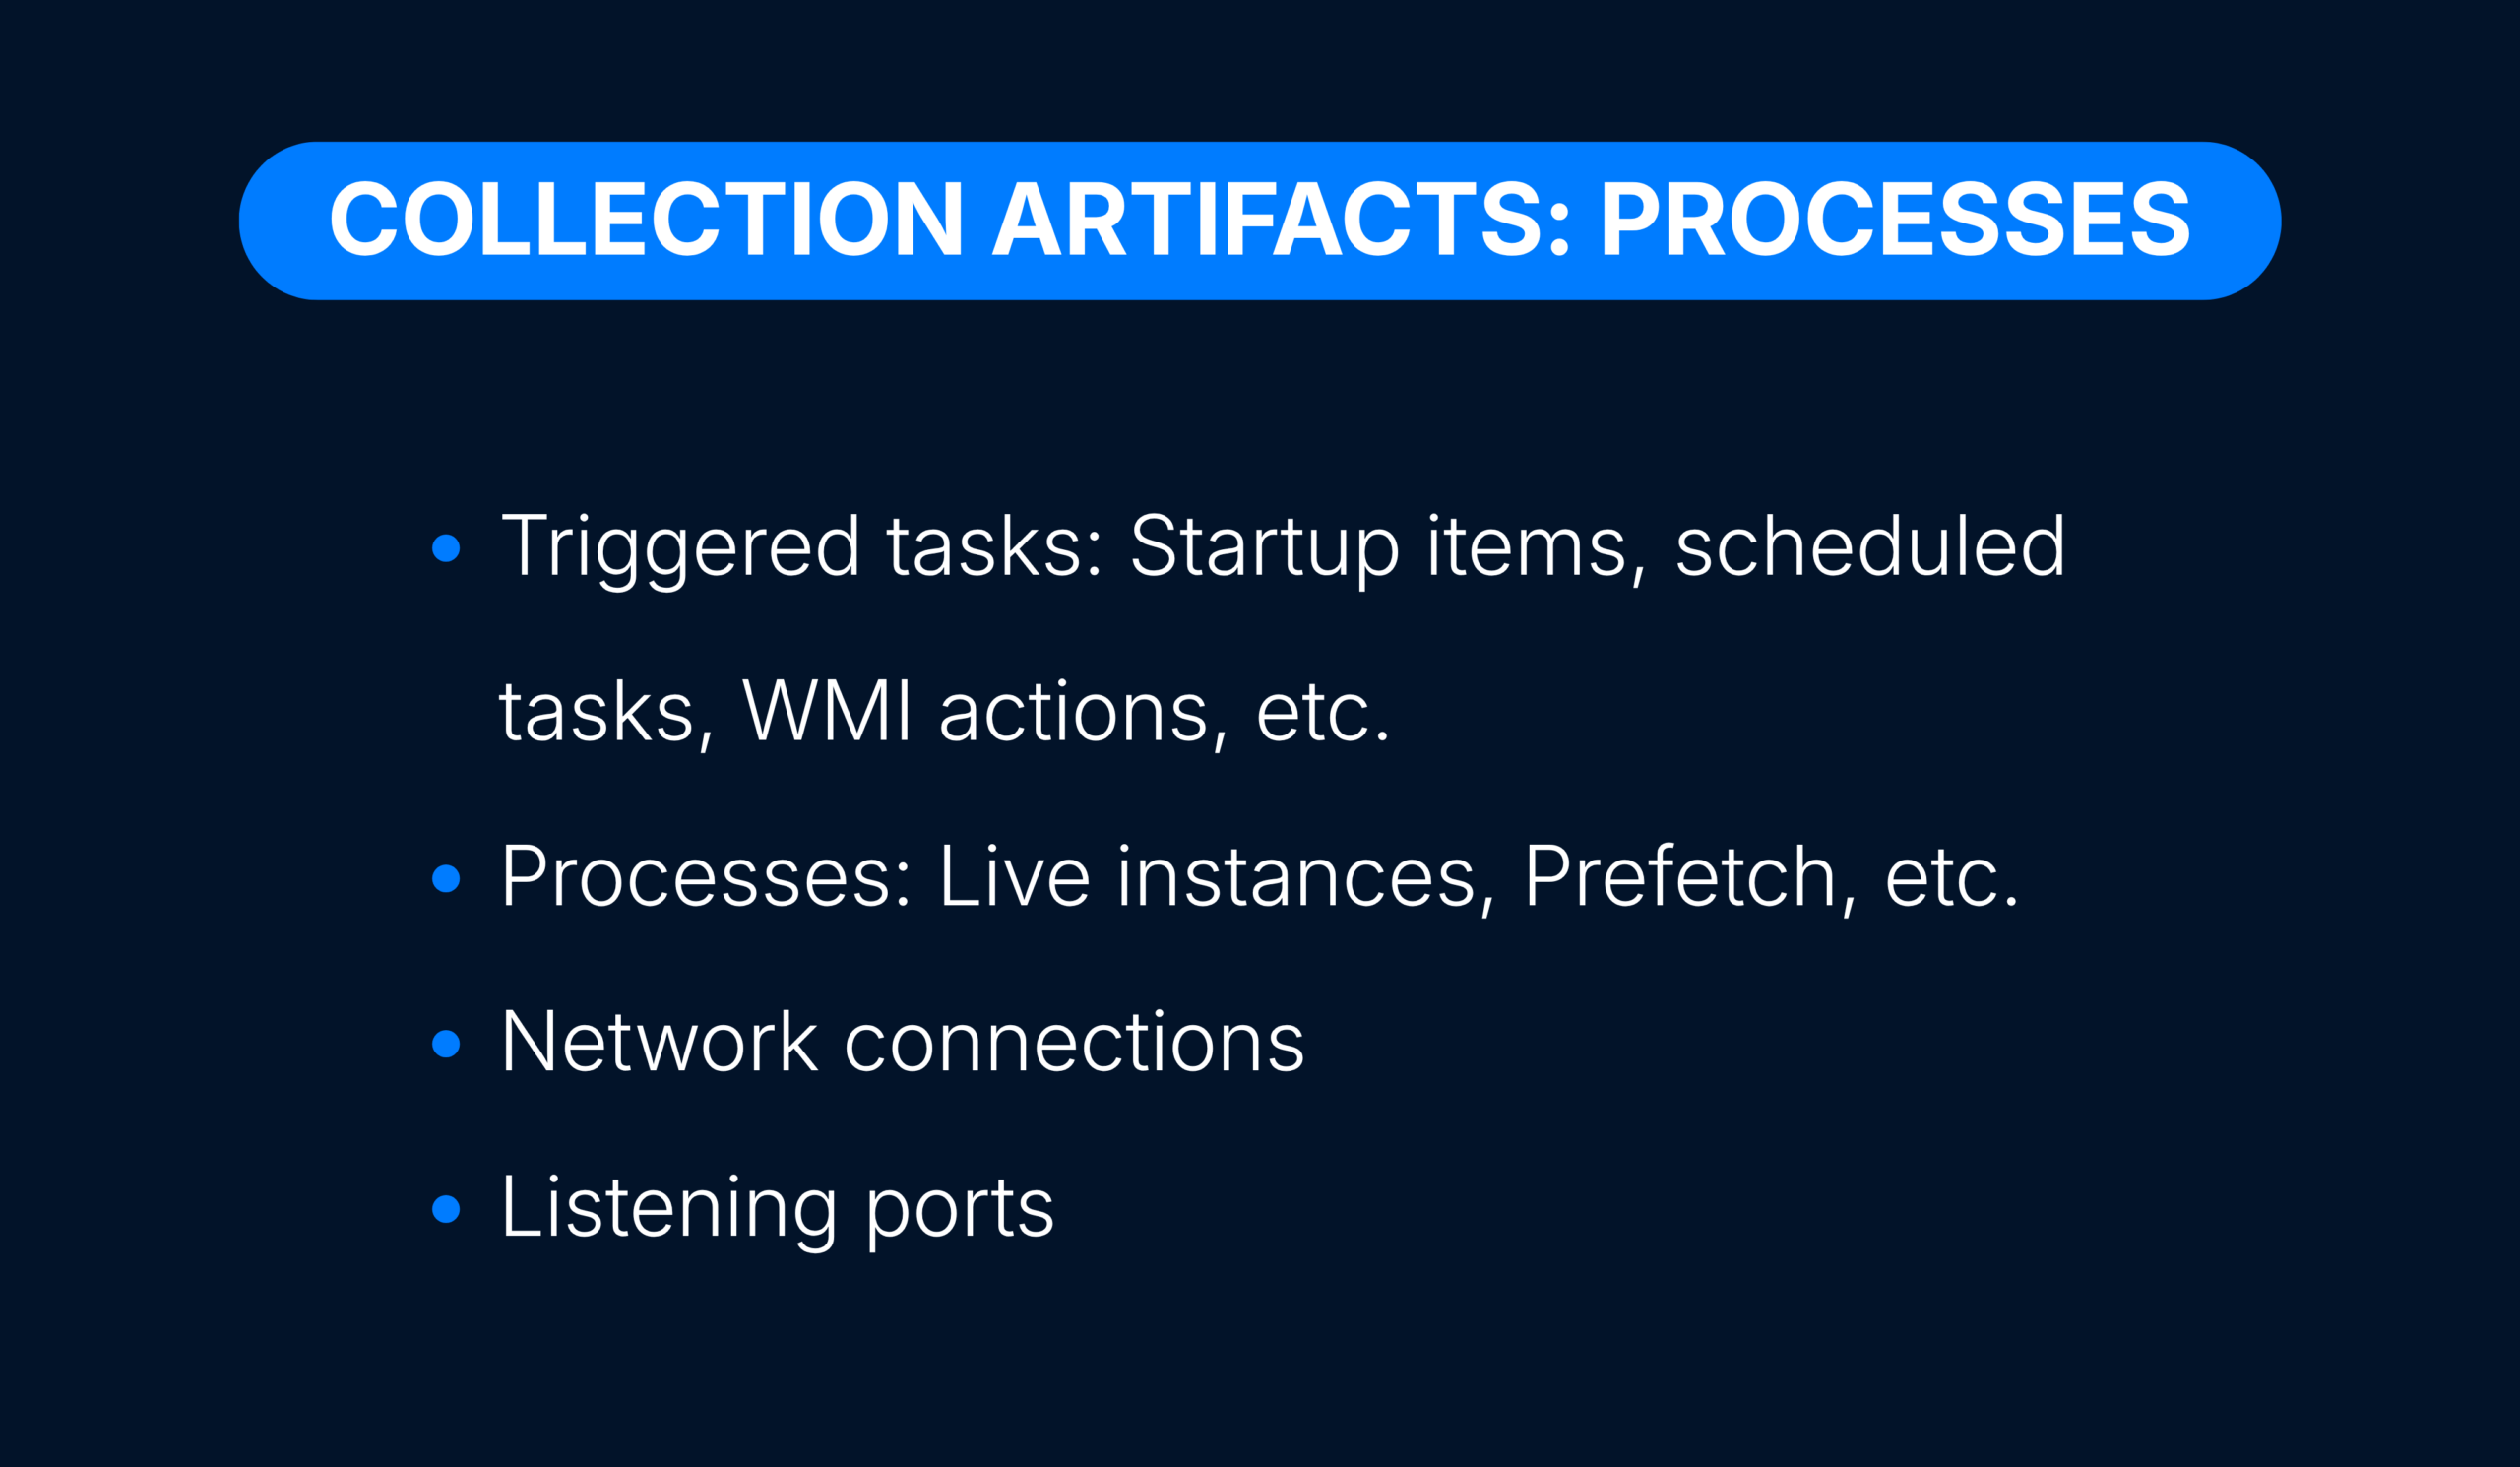
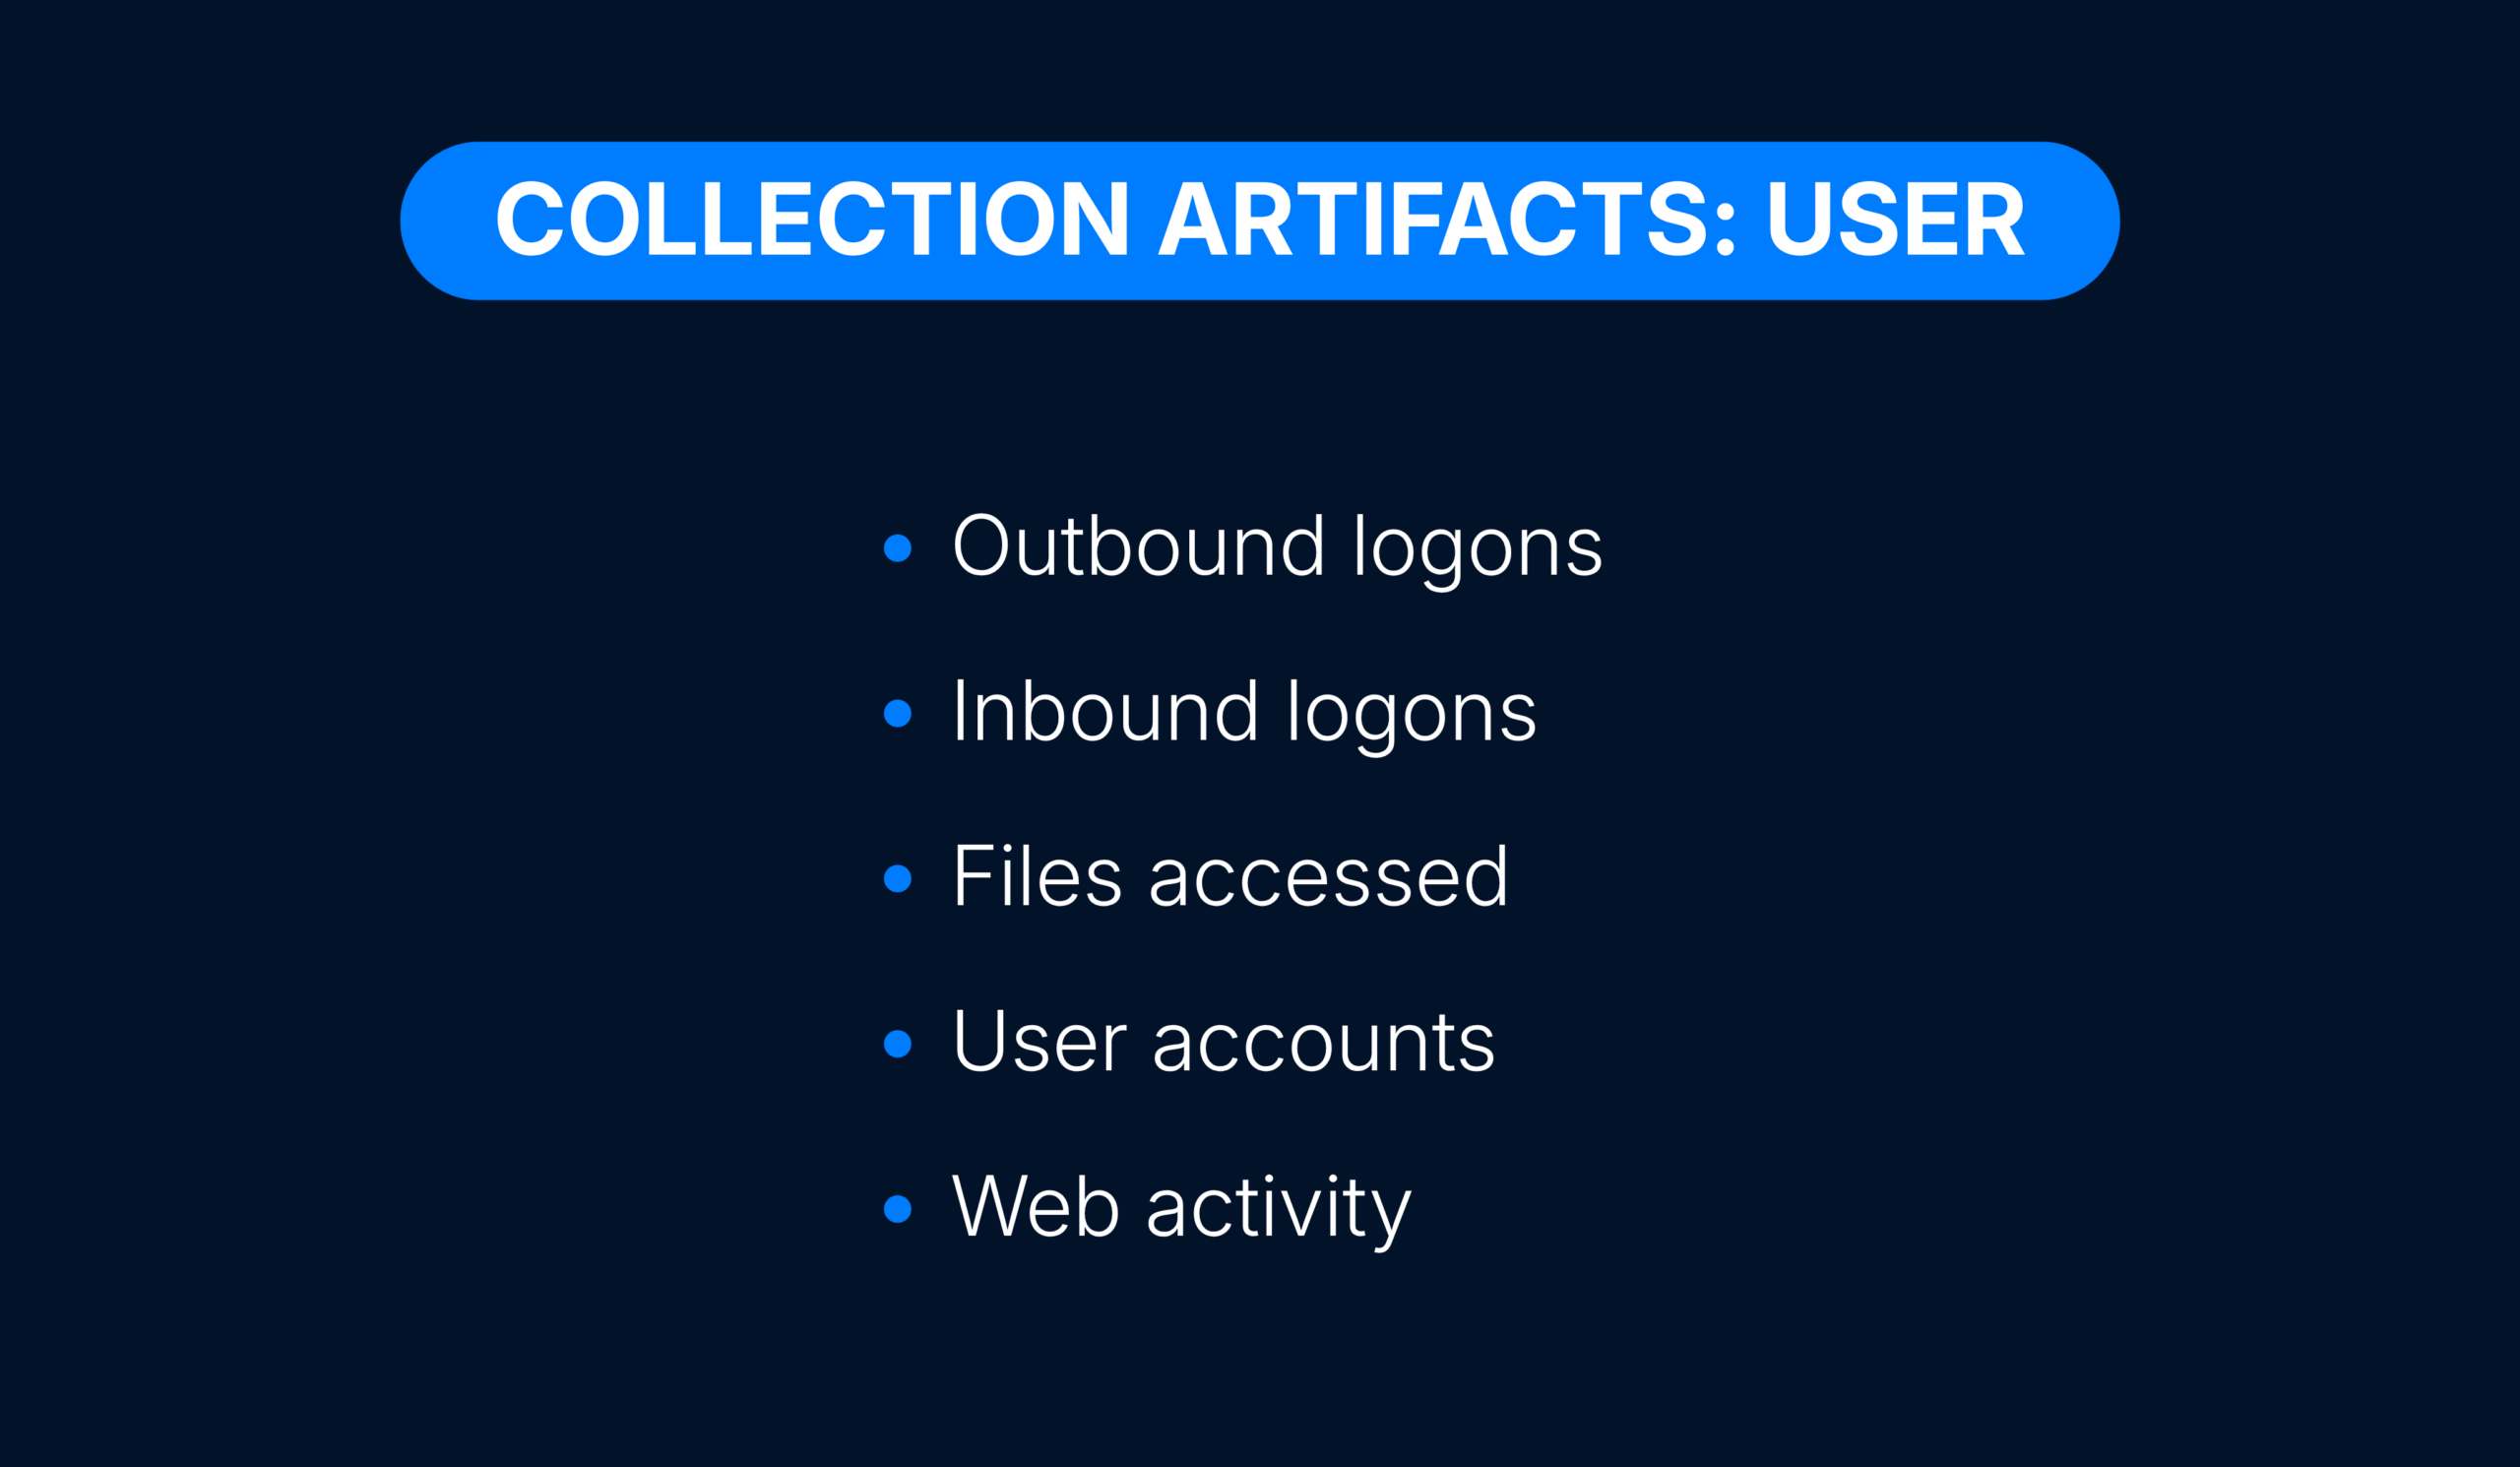
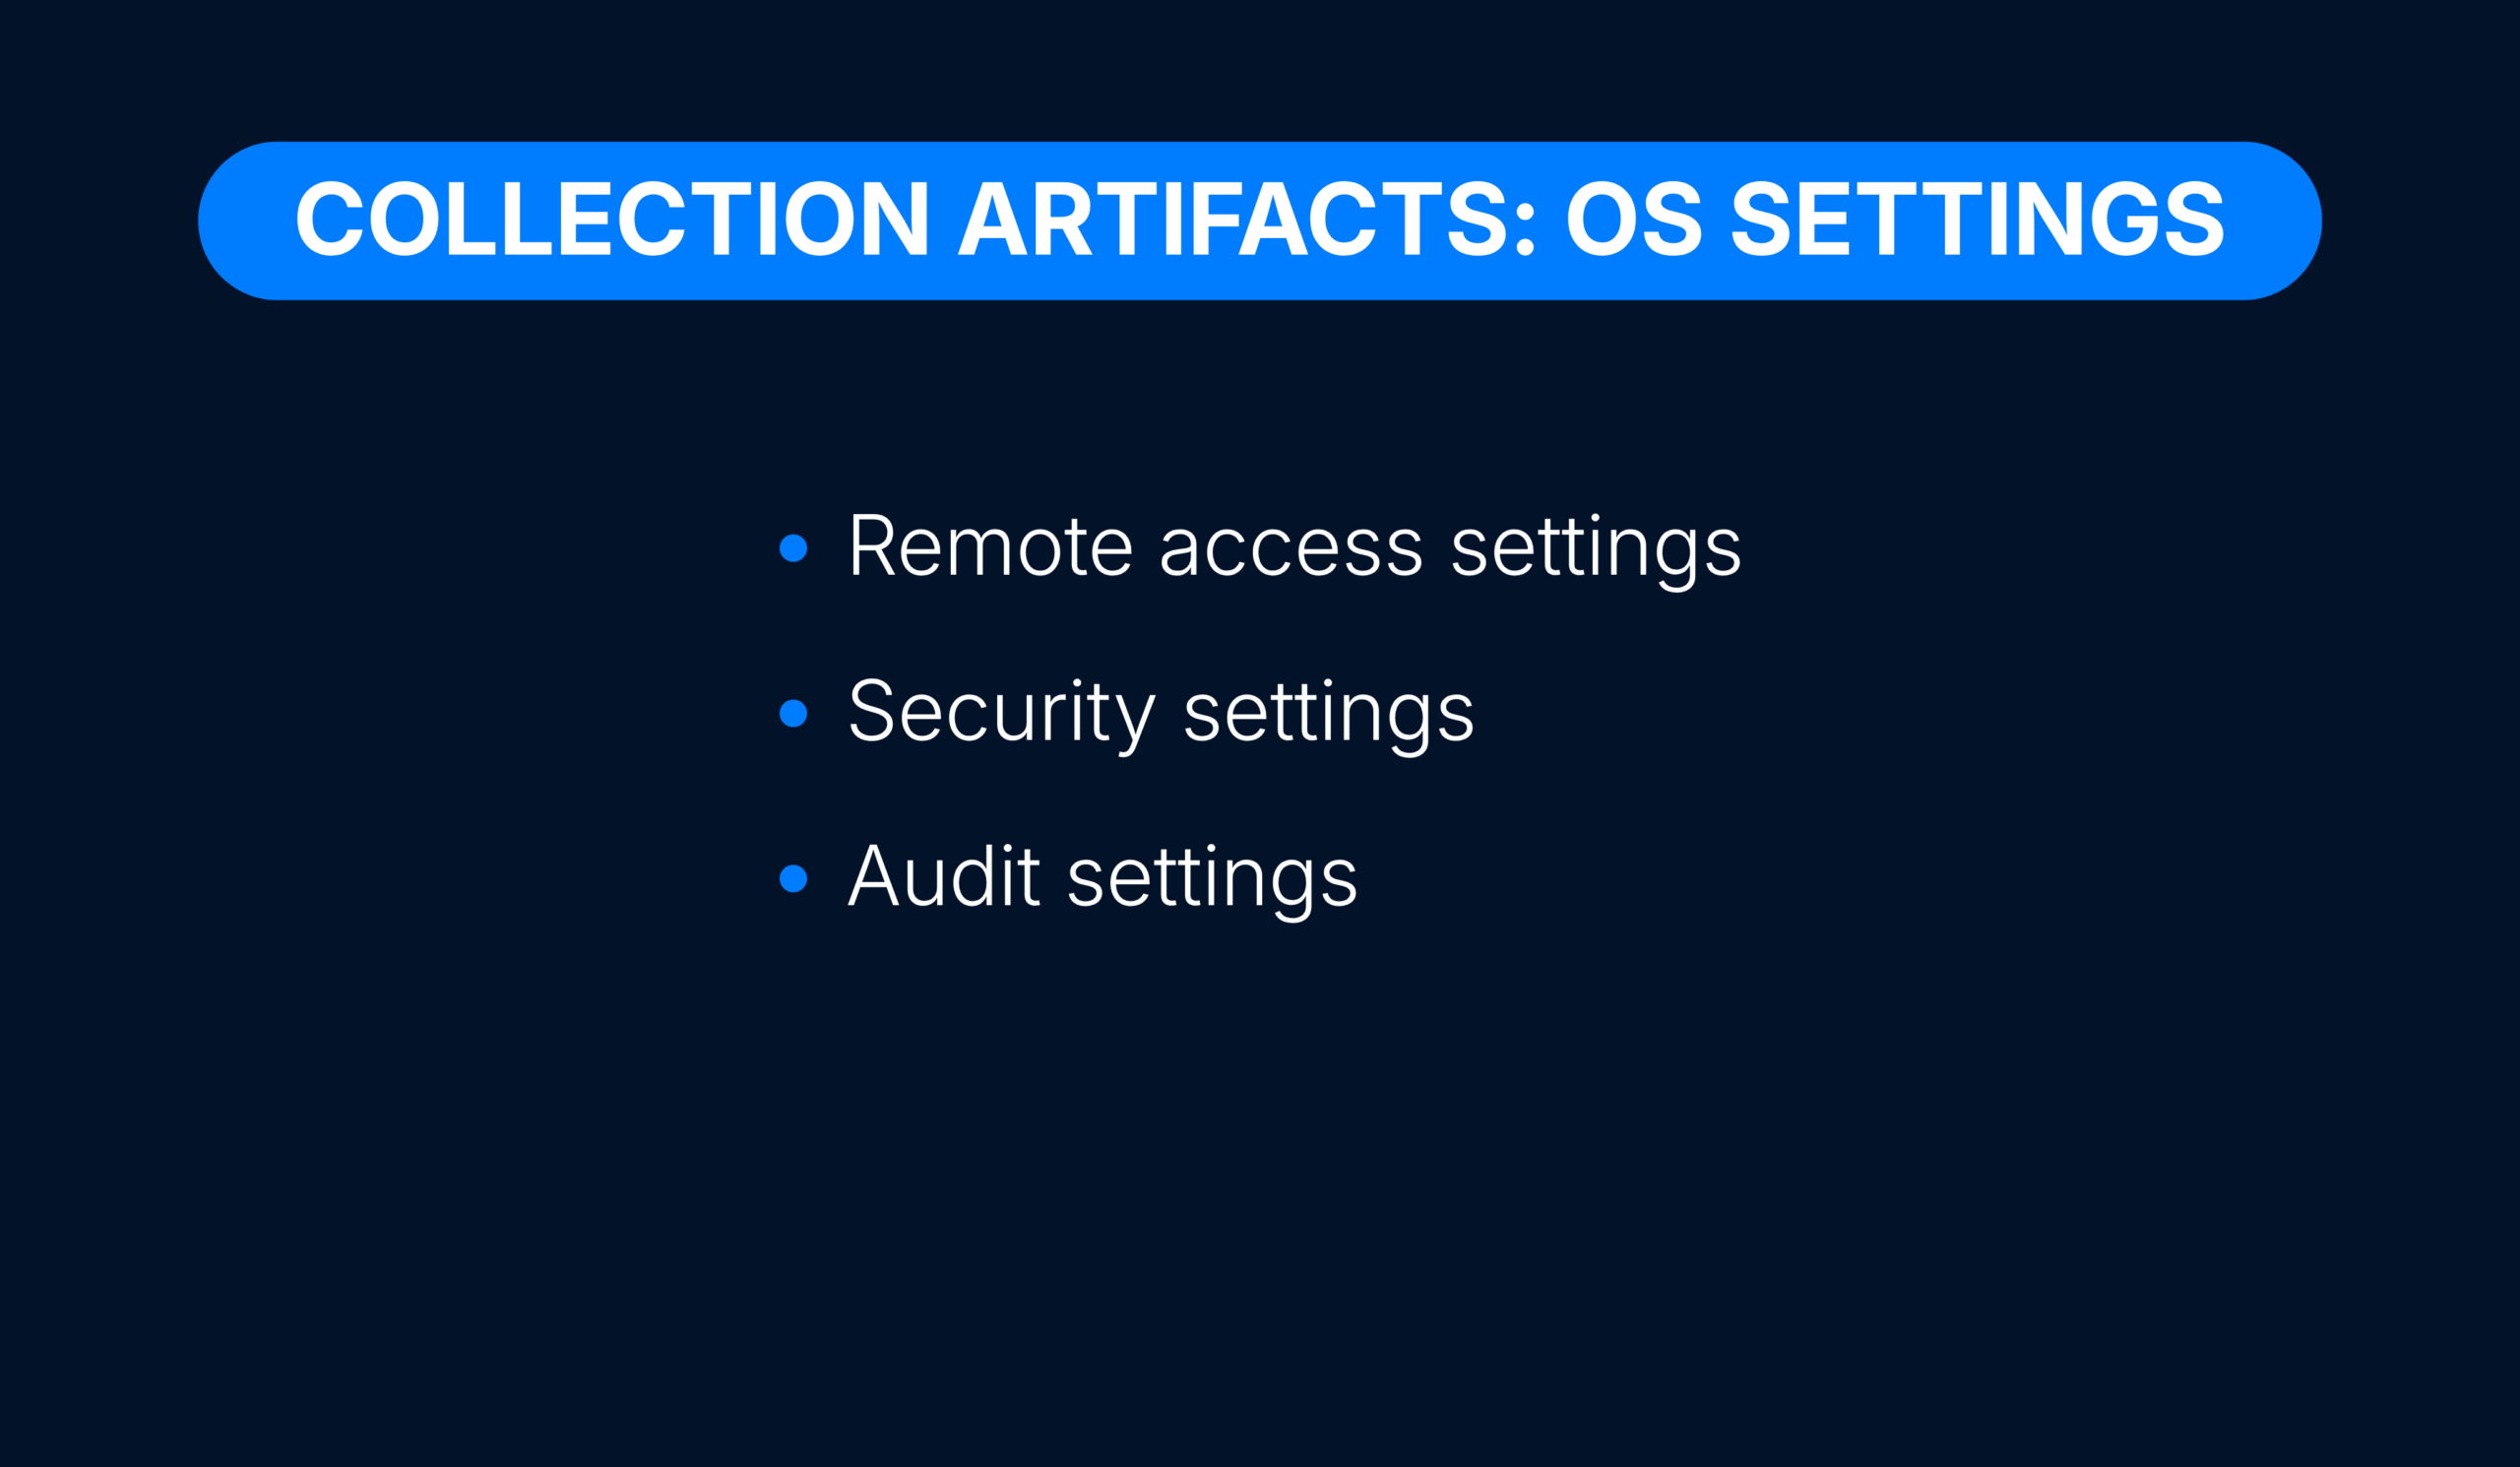
Cyber Triage has a native, Adaptive Collector that can be launched directly from the Cyber Triage console, an EDR, or as part of an automated SOAR playbook.
The result: You can quickly get DFIR-grade evidence from any endpoint.
AUTOMATED INGEST CAPABILITIES
Cyber Triage imports what you have and collects what you need.
DFIR COLLECTION + IMPORT
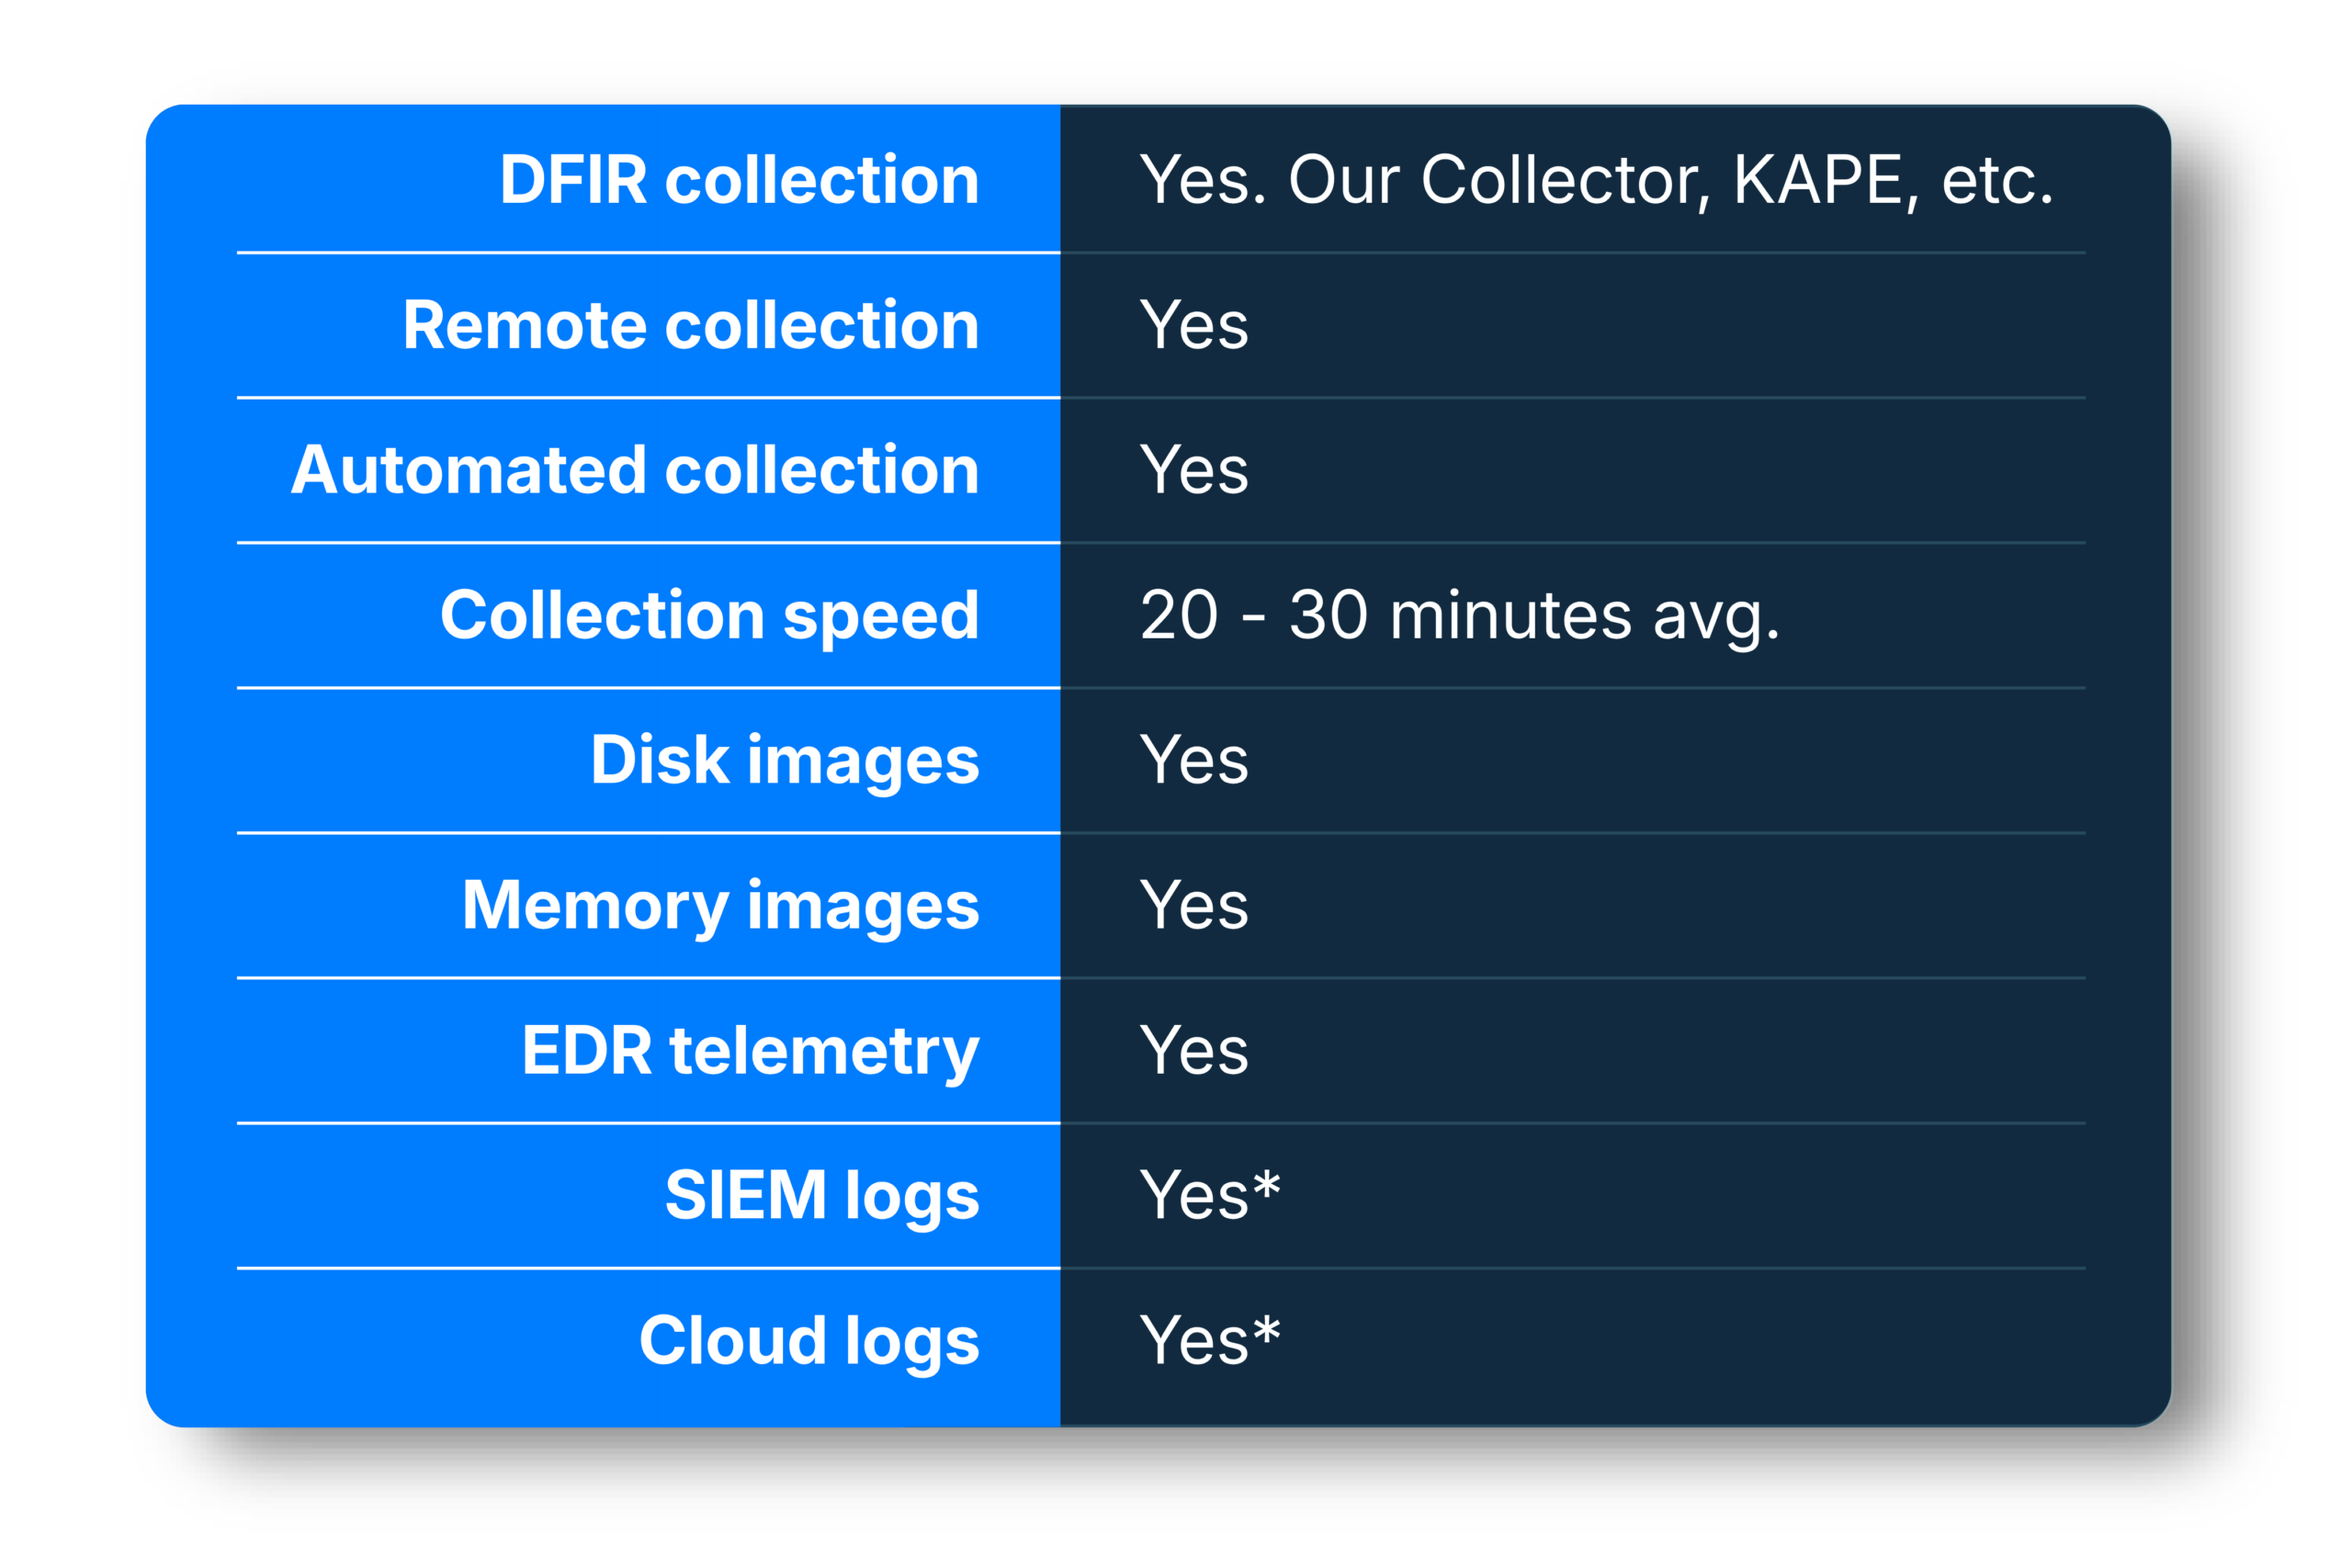
Cyber Triage has its own Adaptive Collector and can import data from other DFIR collectors, including KAPE and Velociraptor.
REMOTE COLLECTION
Cyber Triage’s Adaptive Collector can execute remote DFIR collections and can be deployed via the console, EDR, PsExec, PowerShell, MS Intune, and more.
FAST COLLECTION
Cyber Triage can execute comprehensive DFIR collections in an average of 20 - 30 minutes, much faster than traditional DFIR platforms like Magnet AXIOM.
DISK IMAGE IMPORT
Cyber Triage can import disk images from Exterro FTK, Belkasoft Triage, and EnCase Imager.
MEMORY IMAGE IMPORT
Cyber Triage can import memory images and process them using Volatility v2 or MemProcFS.
EDR TELEMETRY IMPORT
Cyber Triage can directly import data from Microsoft Defender, SentinelOne, and (coming soon) CrowdStrike.
CLOUD LOG IMPORT
Cyber Triage will soon import logs directly from cloud platforms like Microsoft 365, Azure, and AWS.
SIEM LOG IMPORT
Cyber Triage will soon import data directly from SIEMs like Splunk and IBM QRadar.
THE IMPACT OF AUTOMATED INGEST
Investigations at a major industrial manufacturer were taking too long. Part of the problem: They couldn’t collect the evidence they needed fast enough.
Then they found Cyber Triage.
“I have used CyberTriage in live incidents and the speed and what it does has been great! Extremely pleased with this software,” said the company’s forensics lead.
WHAT USERS ARE SAYING
TEST OUR PROMISE
See how Automated Ingest accelerates your investigations with a free with a free, 1-week evaluation.
*SIEM and cloud log import coming soon.