GET YOUR TEAM WORKING TOGETHER
Collaborative Investigations connects your team and your tech.
Your DFIR control tower.
Collaborative Investigations provides a shared DFIR workspace for your team and connects Cyber Triage to the rest of your tech stack.
Investigate with all your resources working together.
INVESTIGATE WITH YOUR ENTIRE TEAM
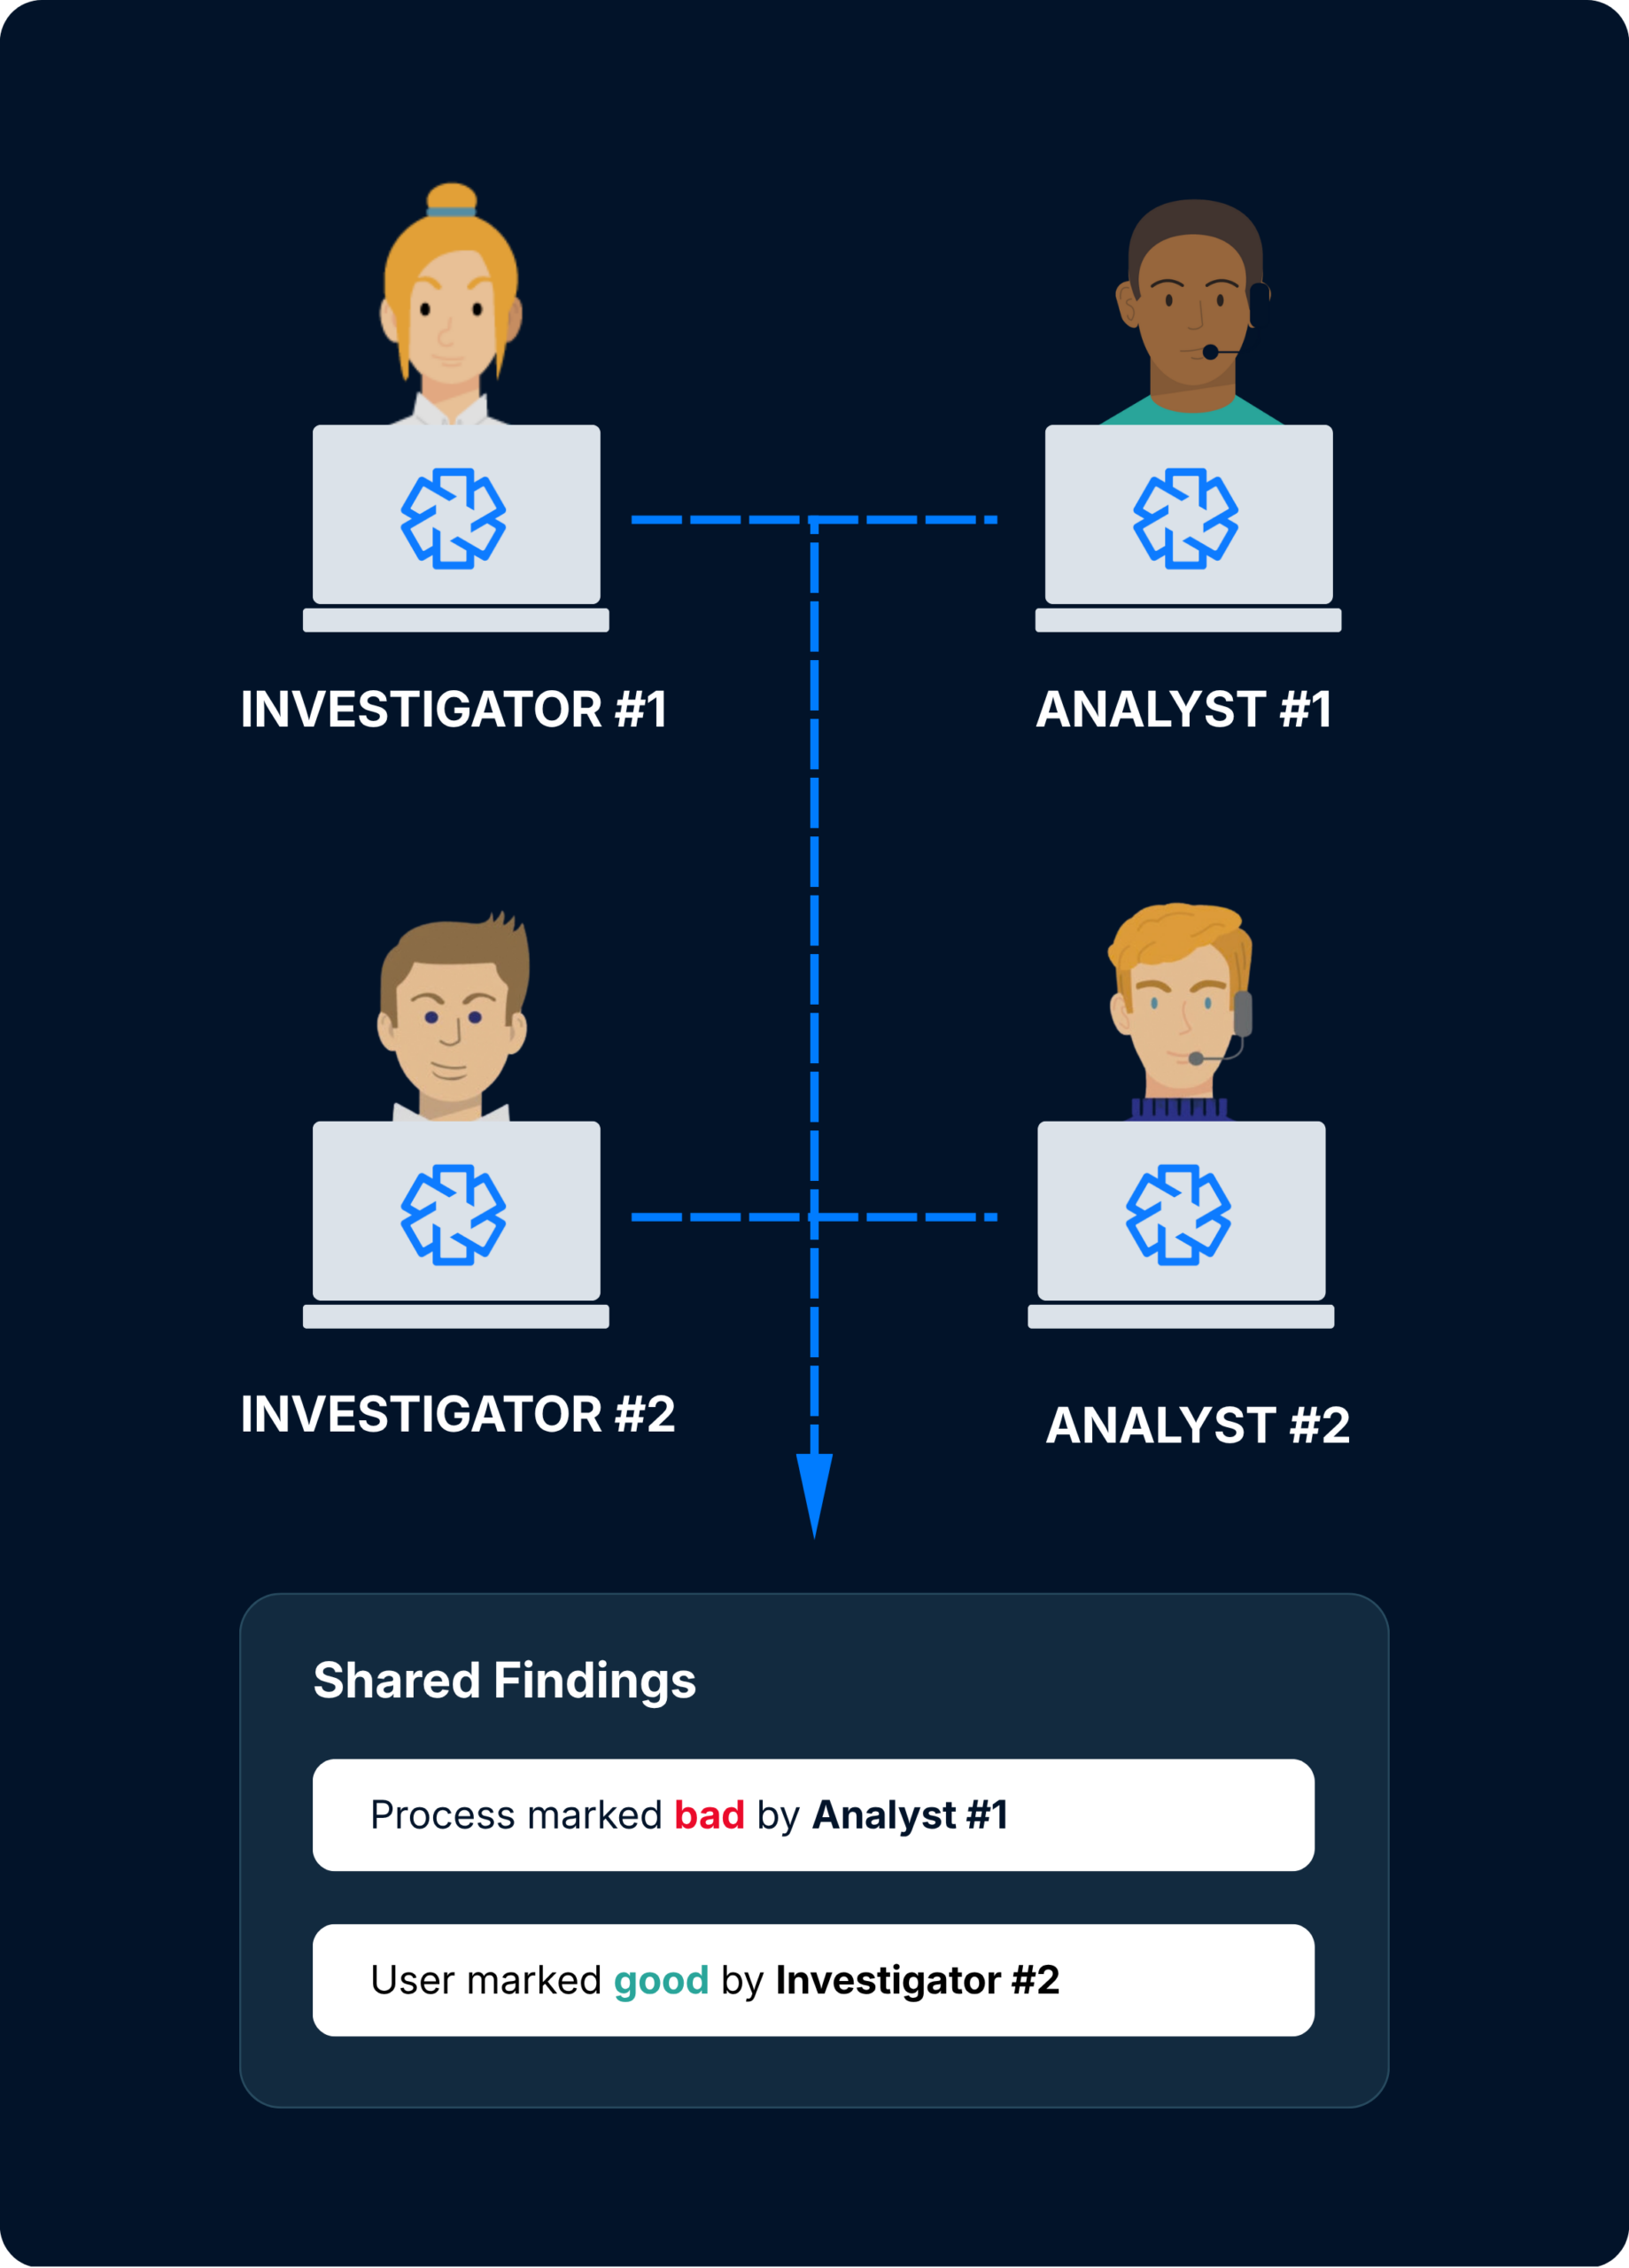
Cyber Triage allows teams of 100+ to work on the same incident at the same time. Every step creates shared progress. Every past finding informs the present. Every investigator can easily forward data or get a second opinion.
The result: Your team’s investigations are faster, more comprehensive, and more efficient.
CONNECT YOUR TECH STACK
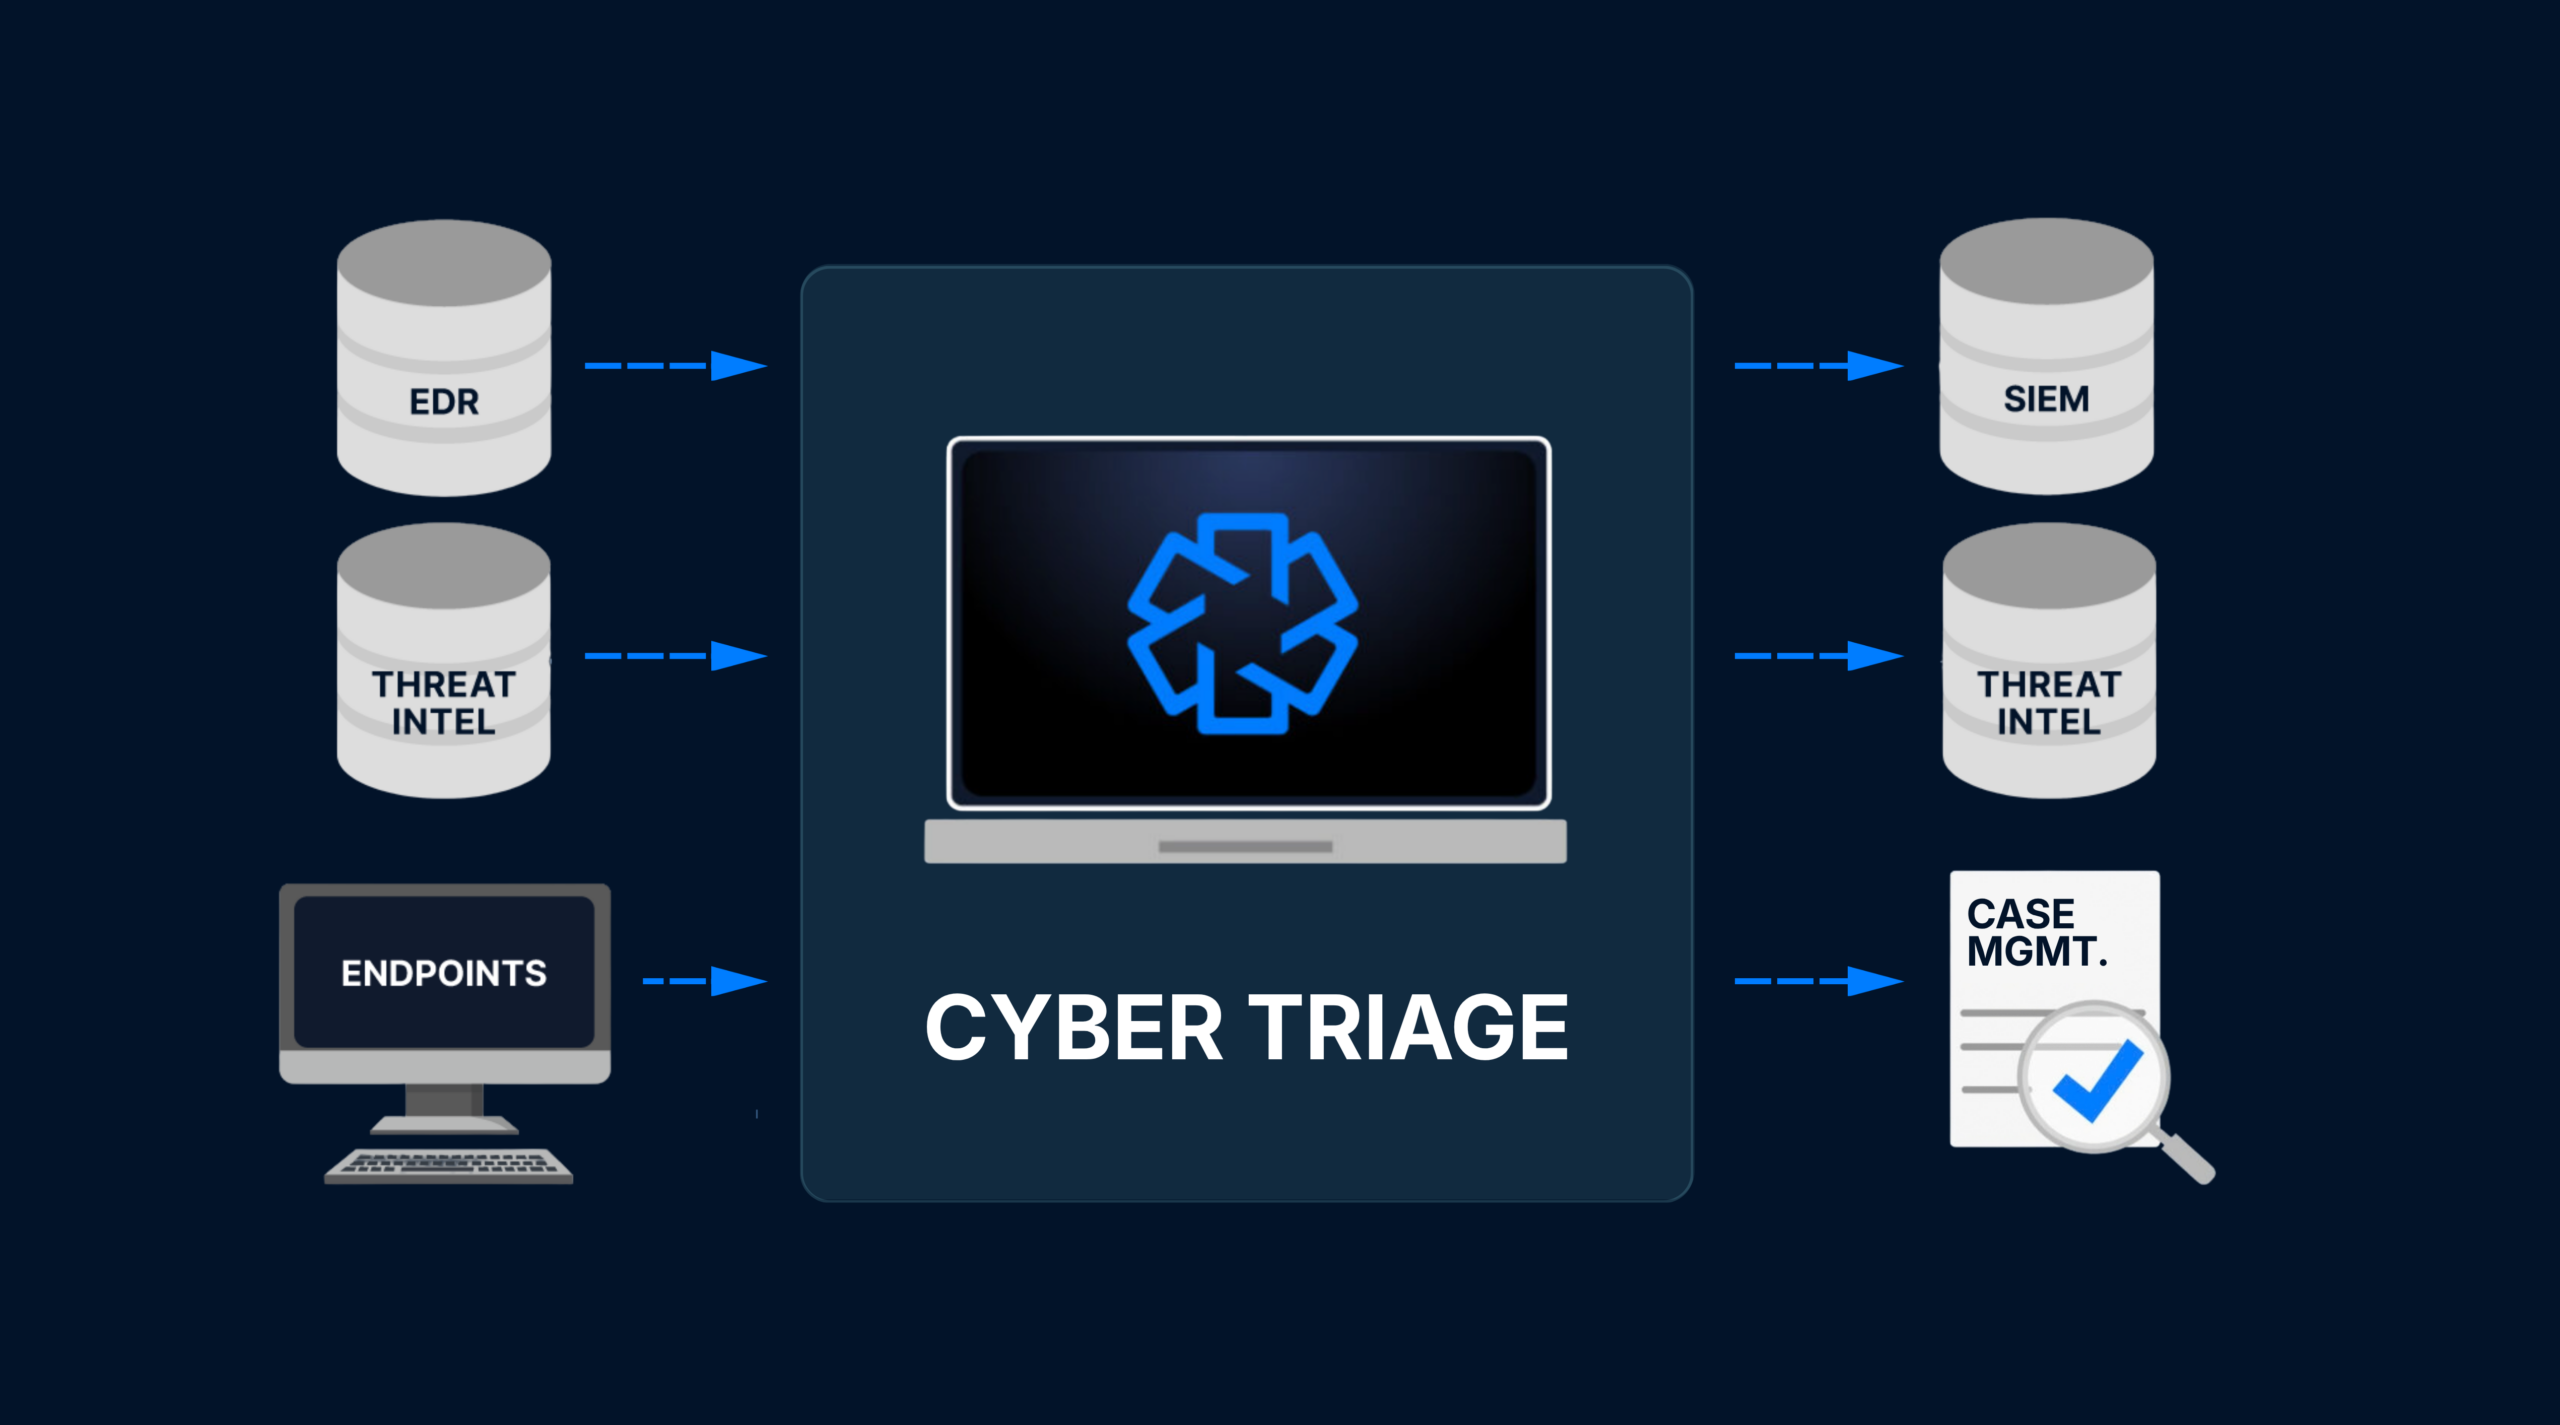
Cyber Triage integrates with your entire tech stack. EDR, SIEM, SOAR, case management, and (coming soon) threat intel platforms all connect with our console to create a streamlined investigation workflow.
The result: Your data flows quickly, and your conclusions are based on all your evidence.
COLLABORATIVE INVESTIGATION CAPABILITIES
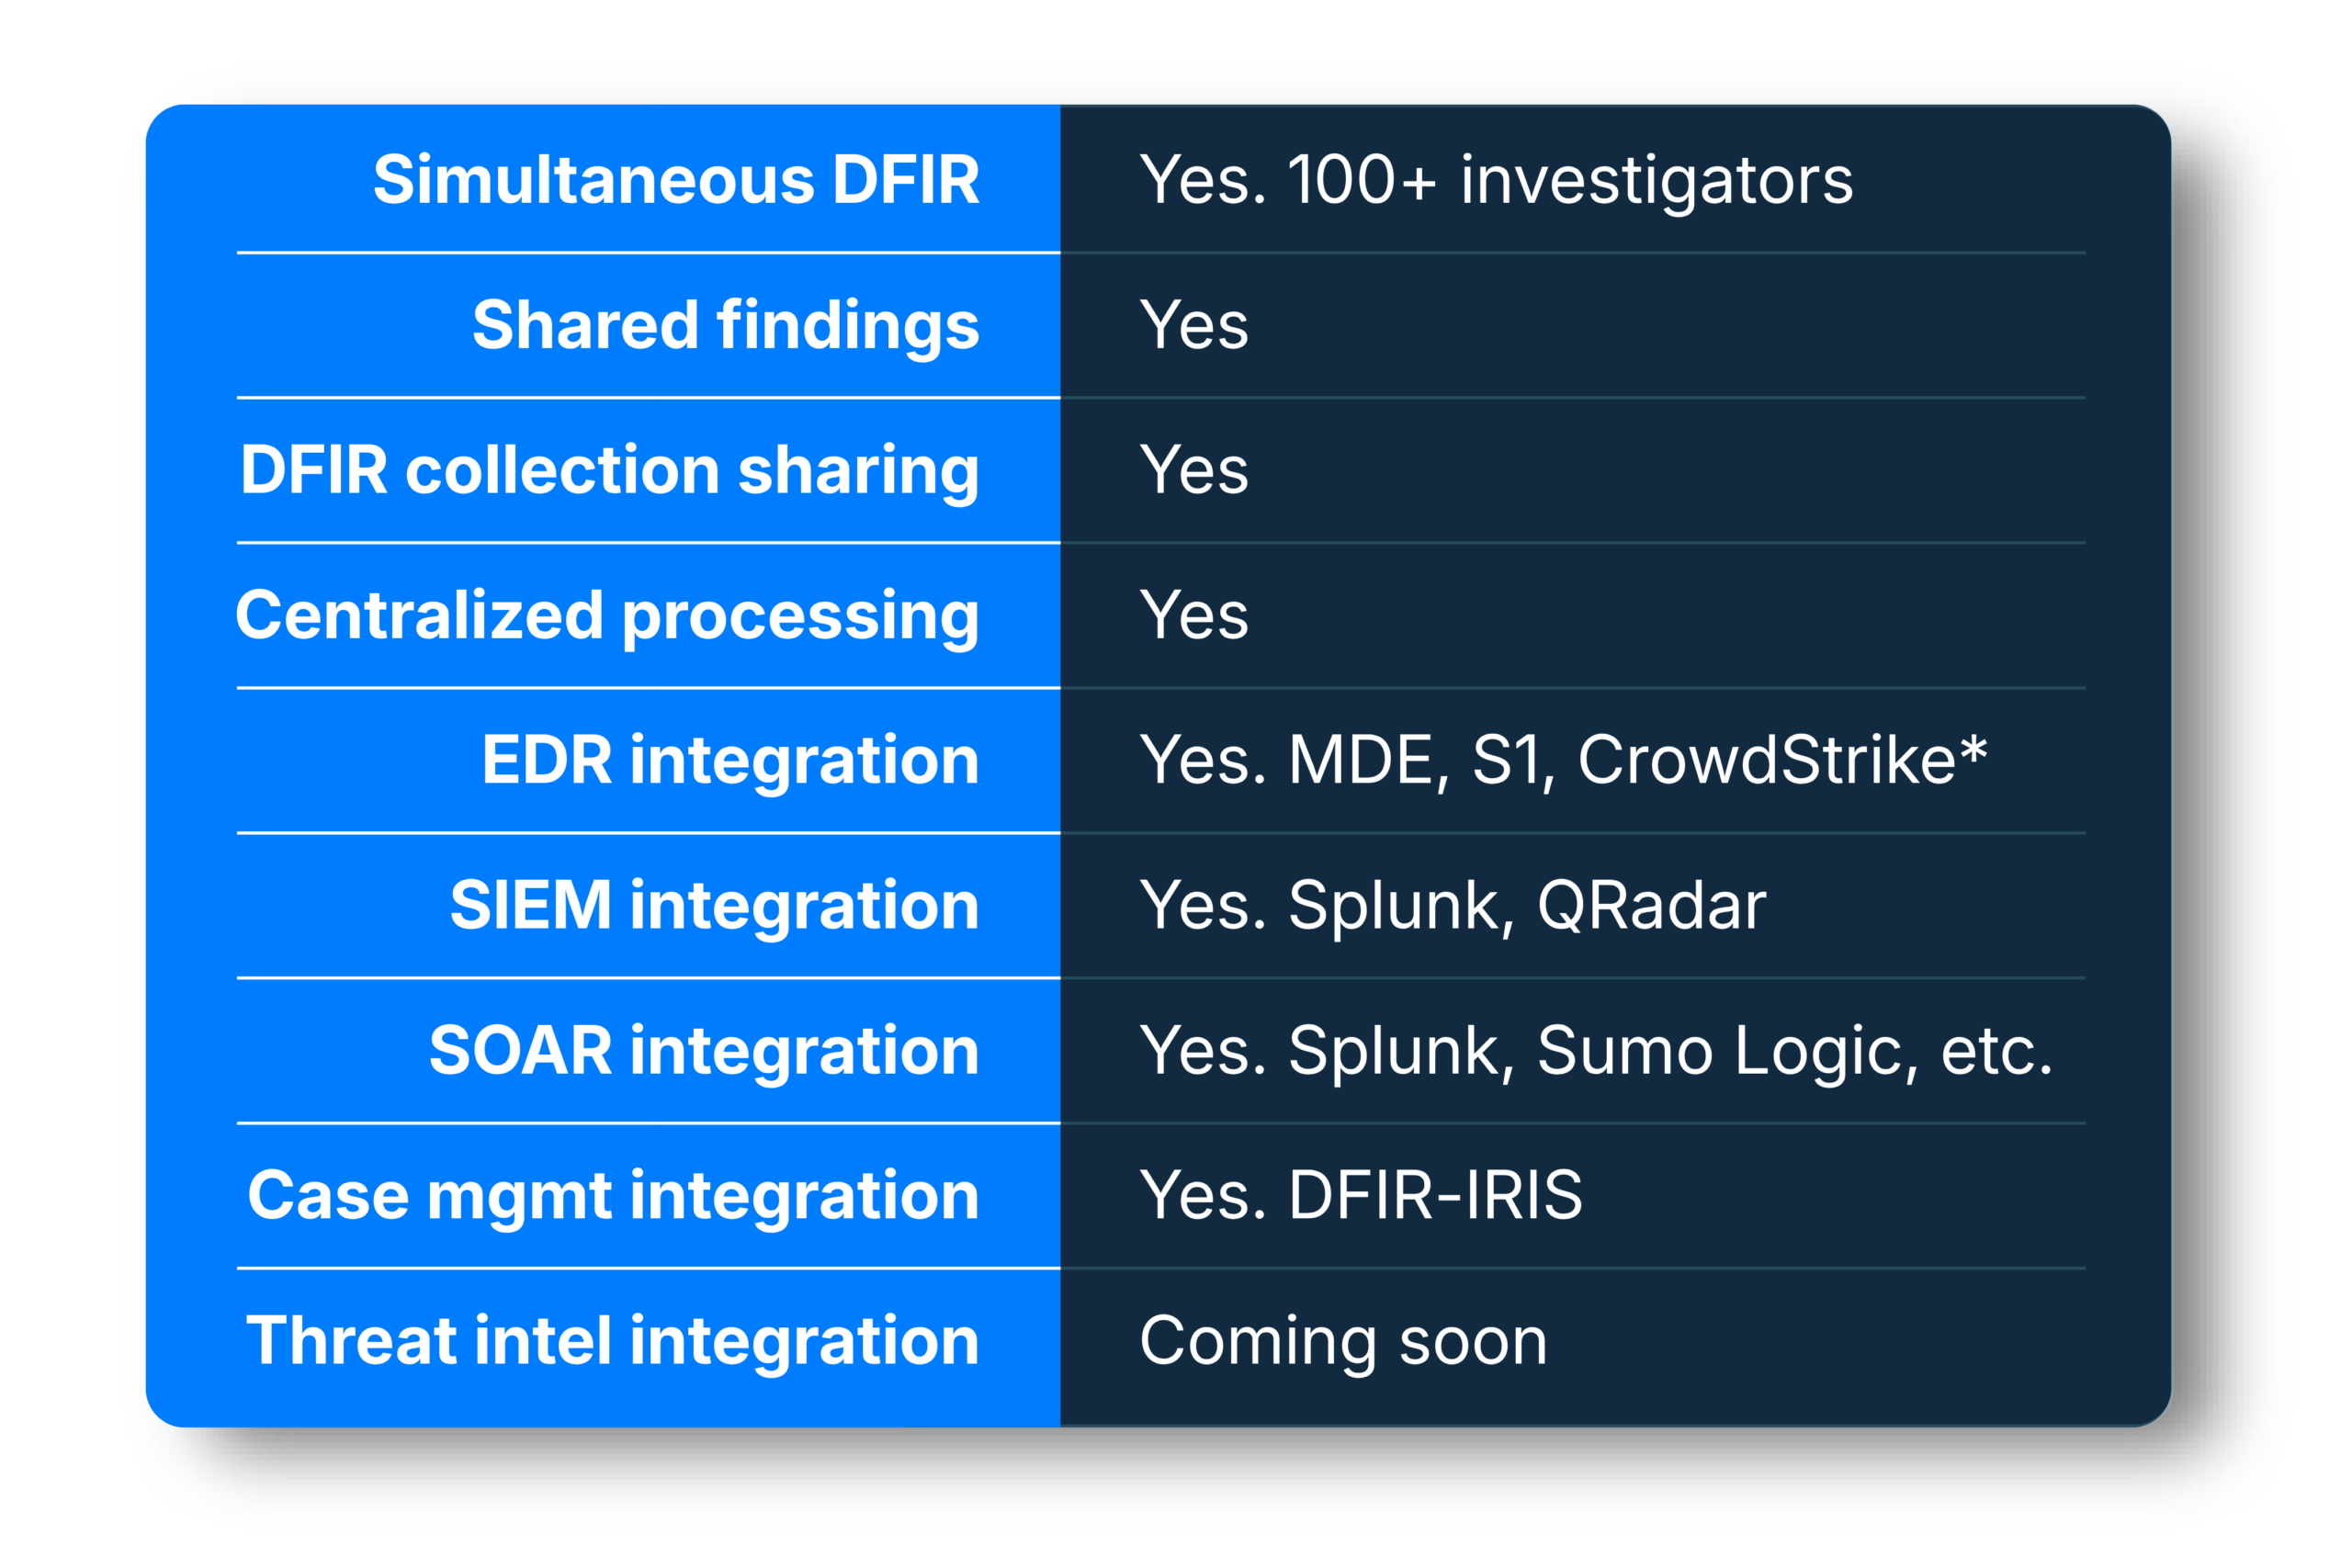
Cyber Triage is the most integrated and collaborative DFIR platform.
SIMULTANEOUS DFIR
Cyber Triage allows large teams of analysts and investigators (100+) to work on incidents at the same time.
SHARED FINDINGS
Cyber Triage is a collaborative investigation environment. Views, data, scores, labels, findings, progress — everything is shared across the team so cases can be closed quickly with minimal duplicate work.
DFIR COLLECTION SHARING
Cyber Triage lets team members share DFIR collections between users and teams for greater efficiency. For example, SOC analysts can forward valid alerts with collections directly to the IR team so they can start analysis immediately.
CENTRALIZED PROCESSING
Cyber Triage has an always-on, shared server for fast and reliable data import and processing. Its enterprise-grade, multi-threaded database also supports rapid DFIR analysis.
EDR INTEGRATION
Cyber Triage lets team members share DFIR collections between users and teams for greater efficiency. For example, SOC analysts can forward valid alerts with collections directly to the IR team so they can start analysis immediately.
SIEM INTEGRATION
Cyber Triage allows you to import data from SIEMs like Splunk and IBM QRadar. Soon it will have direct data ingest and allow uploading results.
SOAR INTEGRATION
Cyber Triage integrates with SOARs like QRadar, Cortex, Splunk, Swimlane, and Sumo Logic so you can automatically launch investigations for faster response.
CASE MANAGEMENT INTEGRATION
Cyber Triage integrates with case management platforms like DFIR-IRIS so you can easily export results from Cyber Triage into these platforms for future correlations and reporting.
THREAT INTEL INTEGRATION
Cyber Triage will soon support importing IOCs from and uploading IOCs to threat intel systems.
THE IMPACT OF COLLABORATIVE INVESTIGATIONS
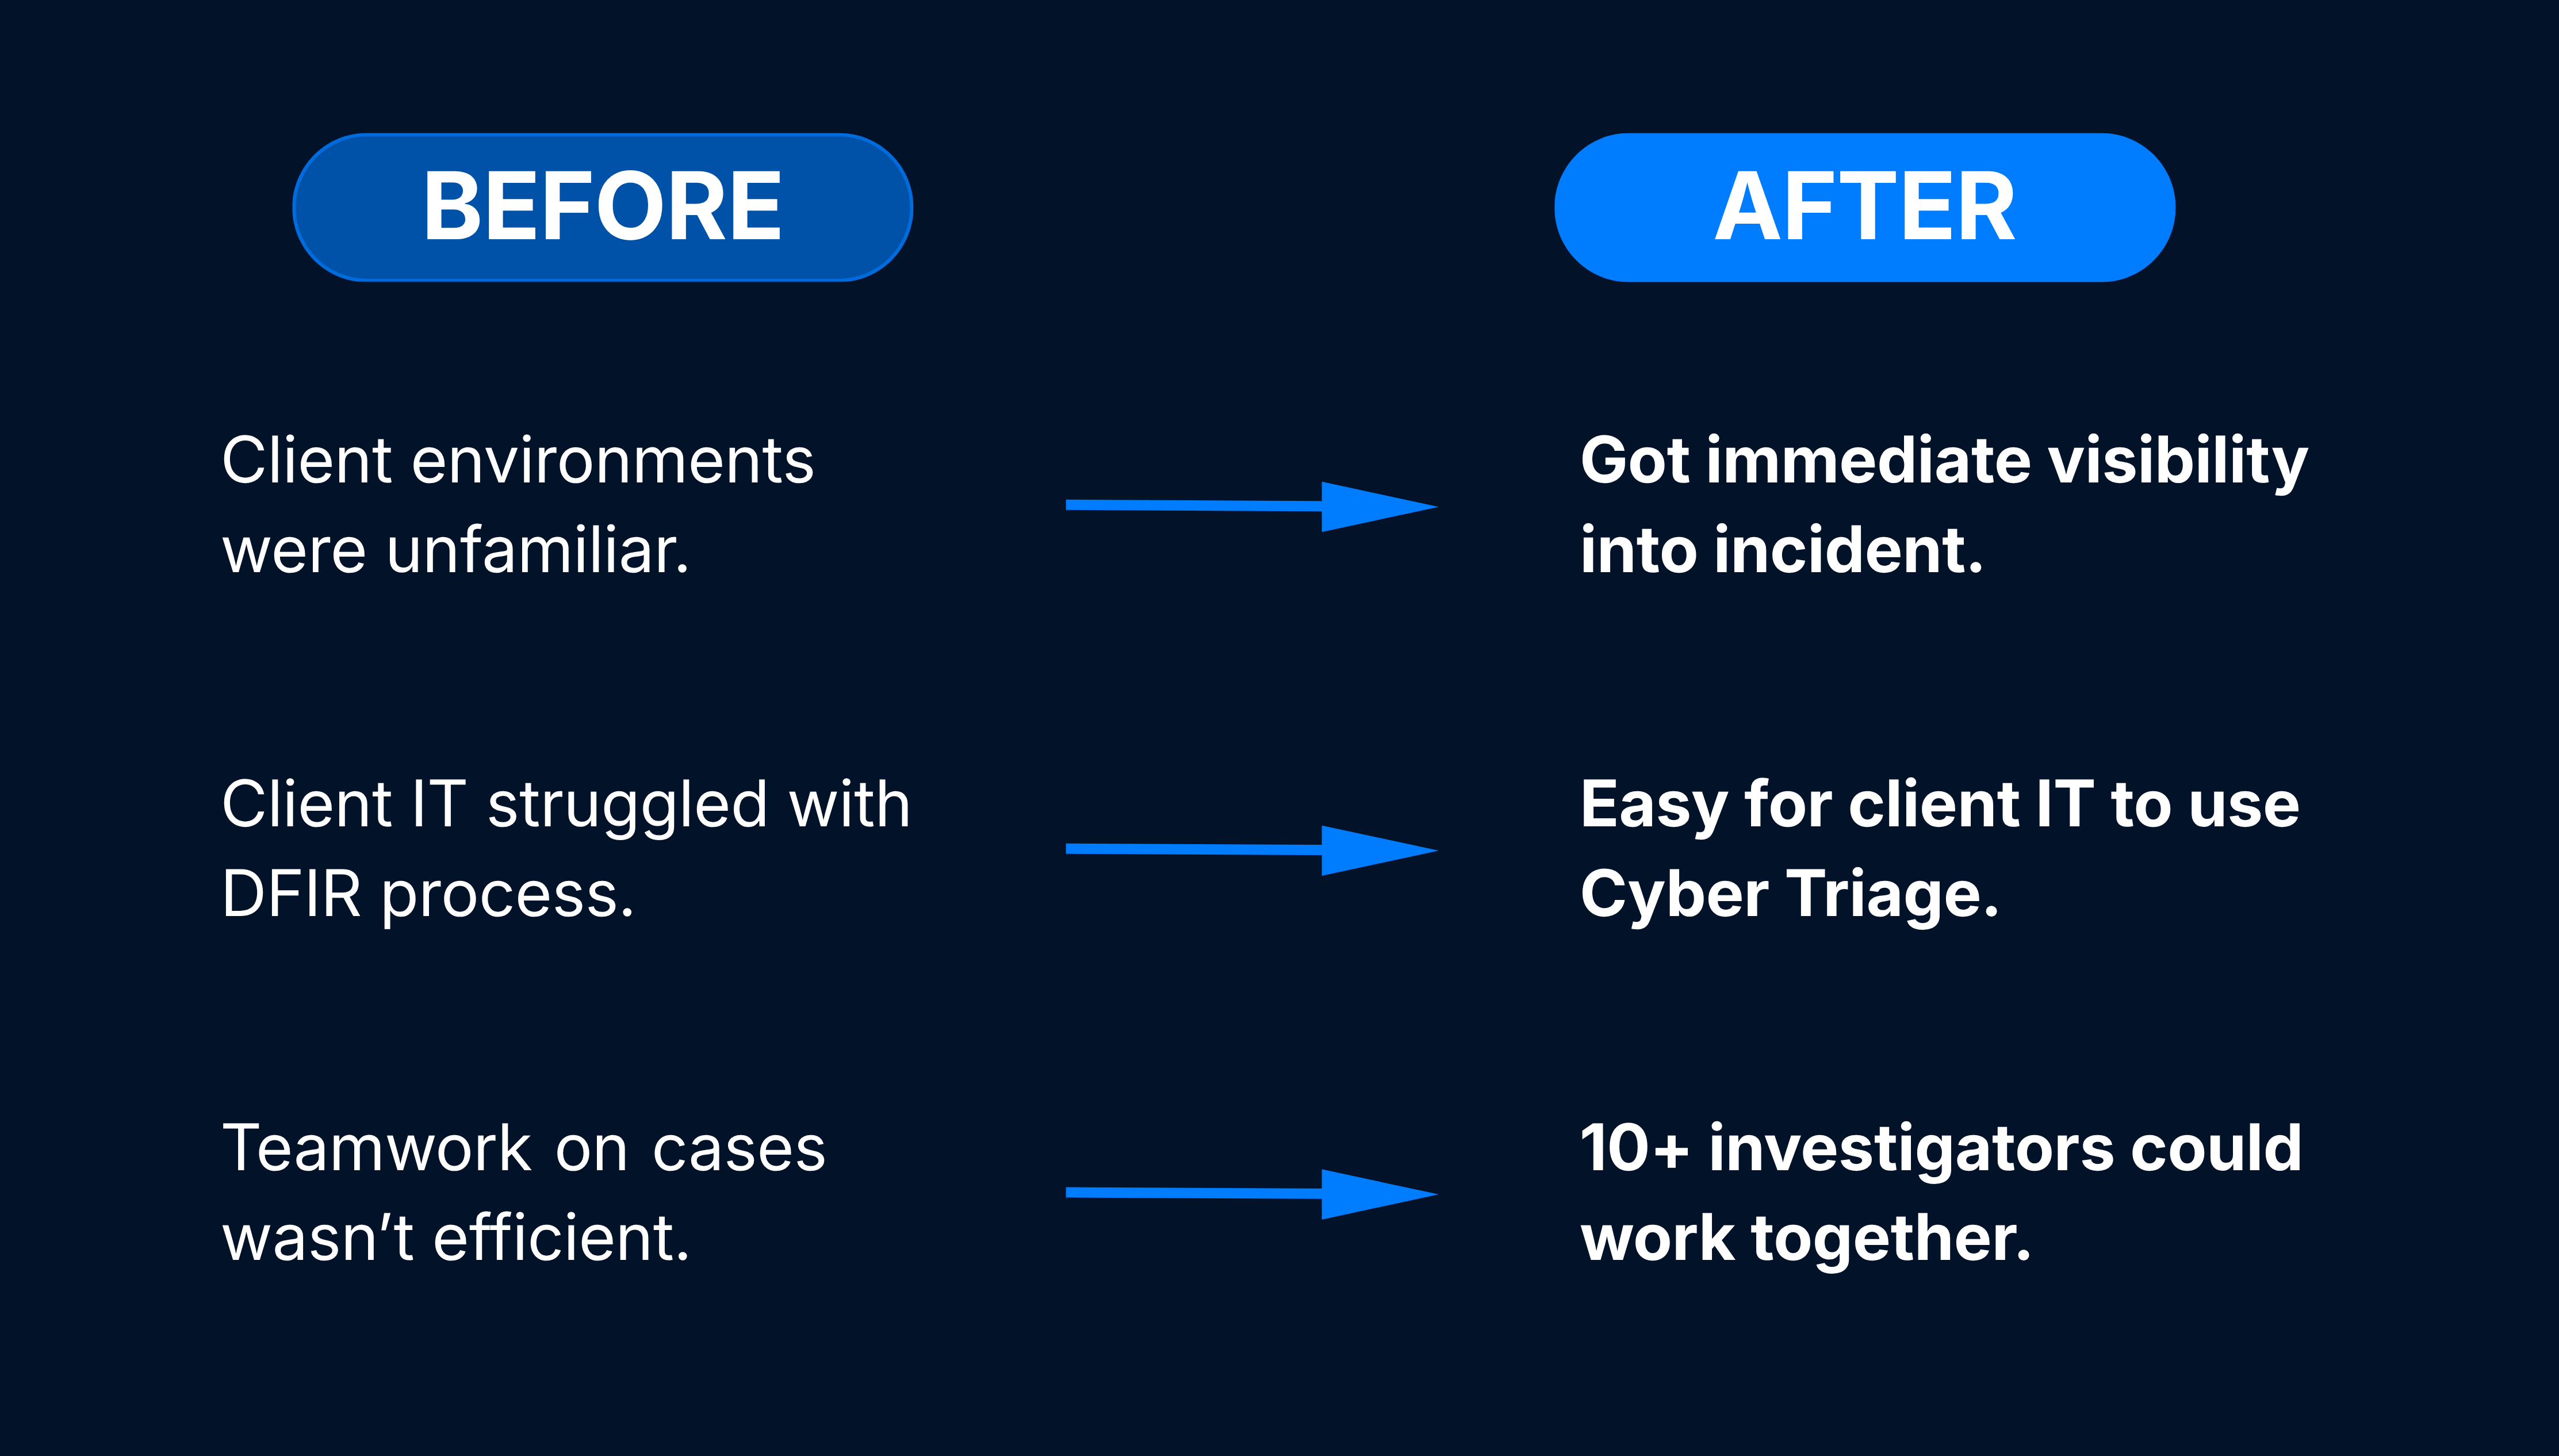
A Fortune 100’s IR consulting team was overloaded with client work and needed to improve efficiency and effectiveness to handle it.
So they tried Cyber Triage.
Cyber Triage enabled collaboration for teams of 10+ and on cases with 120+ hosts. The whole team could work on the same incident simultaneously, sharing everything as they went.
WHAT USERS ARE SAYING
TEST OUR PROMISE
Test Collaborate Investigations by signing up for a trial and requesting collaboration from sales.
*CrowdStrike telemetry ingest coming soon.